Email Verification Protocol: What Chrome's New Origin Trial Means for Email Marketers

Key Takeaways
- The Email Verification Protocol aims to verify email ownership without requiring a traditional verification email.
- Google's Email Verification API brings browser-mediated email verification to Chrome.
- The protocol involves a verifier, browser, and email provider or issuer.
- EVP and SPF, DKIM, and DMARC address different aspects of email verification and authentication.
- Browser-based verification may reduce signup friction but does not guarantee future email deliverability.
- The technology remains in an experimental origin trial, so compatibility and fallback methods are important.
- Email marketers should monitor its development while maintaining existing email authentication and deliverability practices.
Email verification is a common step in website registration, account creation, and subscription forms. Traditionally, users must receive a one-time passcode (OTP) or click a magic link, leave the website, open their inbox, and return to complete the process. Every additional step can create friction and increase the chances of users abandoning the signup process.
Google's proposed Email Verification Protocol introduces a different approach to this familiar problem. Its development is worth following for website owners, developers, and email marketing teams because it could change how businesses verify email ownership and manage user registration workflows. It also raises important questions about browser compatibility, email provider support, and the role of traditional verification methods.
Email Verification API vs Email Verification Protocol: Understanding the Difference
The terms Email Verification API and Email Verification Protocol are closely connected, but they describe different aspects of browser-based email verification.
Google Chrome uses the term Email Verification API when referring to its browser-facing proposal. The Email Verification Protocol (EVP) describes the underlying process through which a browser obtains a signed verification token from an email identity provider and presents it to a website.
In simple terms, the API provides the browser integration, while the protocol defines how the verification process works between the browser, identity provider, and website.
How Are They Related?
| Aspect | Email Verification API | Email Verification Protocol (EVP) |
|---|---|---|
| Meaning | Browser-facing API proposal | Underlying verification protocol |
| Main role | Enables browser-mediated verification | Defines the token-based verification flow |
| Key participants | Browser, website, email provider | Verifier, browser, issuer |
| Purpose | Integrates verification into website forms | Establishes proof that a user controls an email address |
| Documentation | Chrome and WICG API documentation | WICG specification and IETF Internet-Draft |
Both are designed to reduce reliance on traditional email verification links and OTPs by allowing a browser to obtain verification proof through a participating identity provider.
It is important to understand that this is different from email authentication protocols such as SPF, DKIM, and DMARC. Those protocols help receiving mail servers authenticate messages and evaluate sender identity, whereas EVP focuses on verifying a user's control of an email address during an online interaction.
Where Can the Email Verification Protocol Be Used?
The Email Verification Protocol can be useful in website and application workflows where confirming email ownership is necessary before allowing a user to proceed. By enabling browser-based verification, it offers an alternative to traditional email confirmation workflows that require users to retrieve an OTP or click a magic link.
Some potential use cases include:
Website Registration and Signup Forms
Websites can use browser-based email verification during account registration to confirm that a user controls the submitted email address. This can reduce the steps involved in completing signup and help minimize interruptions caused by switching between a website and an inbox.
E-commerce Checkout
Online stores can explore email verification during checkout to confirm customer email ownership without requiring a separate verification email. This may help create a smoother checkout experience, particularly when customers are creating accounts or providing contact details.
SaaS Account Creation and Onboarding
Software platforms that require email verification during account creation may benefit from a browser-mediated verification approach. It could simplify initial onboarding by reducing dependence on OTP and magic-link confirmation workflows when the required browser and provider support is available.
Account Recovery and Password Reset
Email ownership verification is also relevant to account recovery workflows. Browser-based verification could provide another way to establish control of an email account before allowing users to proceed with recovery, subject to the application's security requirements and implementation.
Newsletter and Subscription Registration
Websites collecting email addresses for newsletters and subscriptions can explore whether browser-based verification fits their registration process. However, verifying email ownership does not replace consent collection, subscription confirmation requirements, or applicable email marketing compliance obligations.
The suitability of these use cases depends on browser compatibility, participating email providers, implementation requirements, and the availability of a reliable fallback verification method.
Does Email Verification Eliminate the Need for Verification Emails?
The Email Verification Protocol introduces an alternative to traditional email verification methods, but it does not mean that websites can completely eliminate verification emails.
Traditional email verification typically relies on sending a one-time passcode (OTP) or a magic link to the address provided by the user. The user must open their inbox, retrieve the code or click the link, and return to the website to complete the process.
With browser-based email verification, the process can happen without sending a separate confirmation email when the browser, email provider, and verification flow support it.
However, there are important differences between these approaches:
| Email Verification Protocol (EVP) | Uses browser-mediated verification through an email provider | No, when verification succeeds |
| OTP Email Verification | Sends a one-time passcode to the user's inbox | Yes |
| Magic Link Verification | Sends a unique verification link that the user must open | Yes |
| Email Address Validation | Checks whether an email address follows valid formatting and other available validation criteria | No, for basic validation |
Why Traditional Verification Emails Are Still Necessary
Even with the introduction of browser-based verification, websites need to maintain traditional verification methods for situations where the new approach cannot be used.
For example:
- The user's browser does not support the required verification functionality.
- The email provider does not participate in the verification process.
- The browser cannot obtain a valid verification token.
- The verification token is missing, invalid, expired, or cannot be validated.
- The website requires an additional authentication or security step.
This is why fallback verification remains an important part of implementing the Email Verification Protocol.
Rather than completely replacing OTP and magic-link verification, EVP provides another potential option for confirming email ownership while allowing websites to retain existing verification workflows for unsupported scenarios.
What Is the Email Verification Protocol, in Plain Terms
- The Email Verification Protocol (EVP) is a proposed web standard that allows a browser to verify whether a user controls an email address without requiring a traditional verification email. During a supported verification flow, users can select an address from browser suggestions or enter it manually. The browser then communicates with the participating email provider behind the scenes to obtain verification proof. The website can validate this proof without sending a separate OTP or magic link, provided the required browser, provider, and implementation conditions are met.
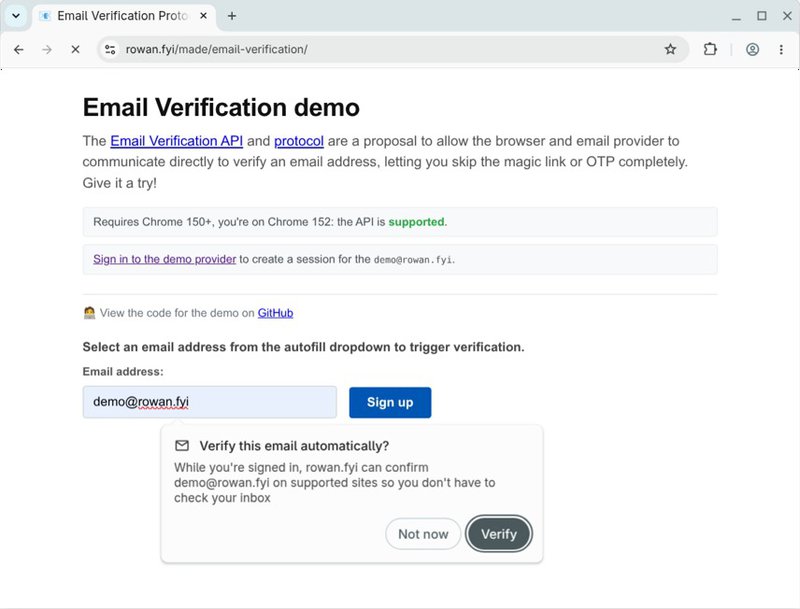
This matters because it's solving a genuinely different problem than the one email authentication protocols like SPF, DKIM, and DMARC solve. Those protocols confirm that a message genuinely came from the domain it claims to represent when it's already in transit. The Email Verification Protocol operates at a completely different point: before any email is sent, confirming that the person filling out a form actually controls the inbox they've typed in.
Email Verification Protocol vs Email Authentication: Two Different Jobs
Because the terminology overlaps so closely with existing deliverability concepts, it's worth being explicit about the distinction.
| Protocol | What It Verifies | What It Verifies | Who Uses It |
|---|---|---|---|
| SPF / DKIM / DMARC | The sending domain is authorized and the message hasn't been altered in transit | At send and receipt time | Mailbox providers evaluating inbound email |
| Email Verification Protocol | The user has an active, authenticated session with their email provider | At form submission, before any email is sent | Websites and applications collecting an email address during sign-up, checkout, or account recovery |
The Email Verification Protocol does not authenticate outbound campaign mail, and it doesn't replace SPF, DKIM, or DMARC in any way. It solves a front-end problem: confirming a user's claimed email address is real and theirs, before your system ever has to send that first confirmation email.
Key Terms in the Email Verification Protocol Flow
Three roles appear throughout the protocol's documentation, and they're worth knowing before the flow makes sense:
| Role | Definition | Example |
|---|---|---|
| Verifier | The site collecting the email address and requesting verification (also called the Relying Party) | An ecommerce checkout page |
| Email Provider | The service hosting the user's email address | gmail.com |
| Issuer | The service managing the account behind that email address (also called the Identity Provider) | accounts.google.com |
In many cases the email provider and issuer are the same organization, but the protocol treats them as distinct roles, since having an email address and having an active, authenticated session for that address's account are two different things.
How the Email Verification Protocol Flow Actually Works
For a site implementing the Email Verification Protocol as a verifier, the flow runs through several discrete steps:
1. A user selects their email address from Chrome's autofill or autocomplete suggestions on a form that includes a hidden token field with a unique, session-bound nonce.
2. The browser looks up an email verification DNS record for the address's domain, which points to the issuer.
3. The issuer confirms it has an active session for that email address and returns an Email Verification Token (EVT), which the browser combines into a signed, key-bound package with the site's origin and the form's nonce.
4. On form submission, that EVT package is sent to the site alongside the rest of the form data.
5. The verifier site validates the token: the expected email address, the nonce, and the signatures from both the browser and the issuer.
6. The user sees a brief notification confirming their provider verified their email address.
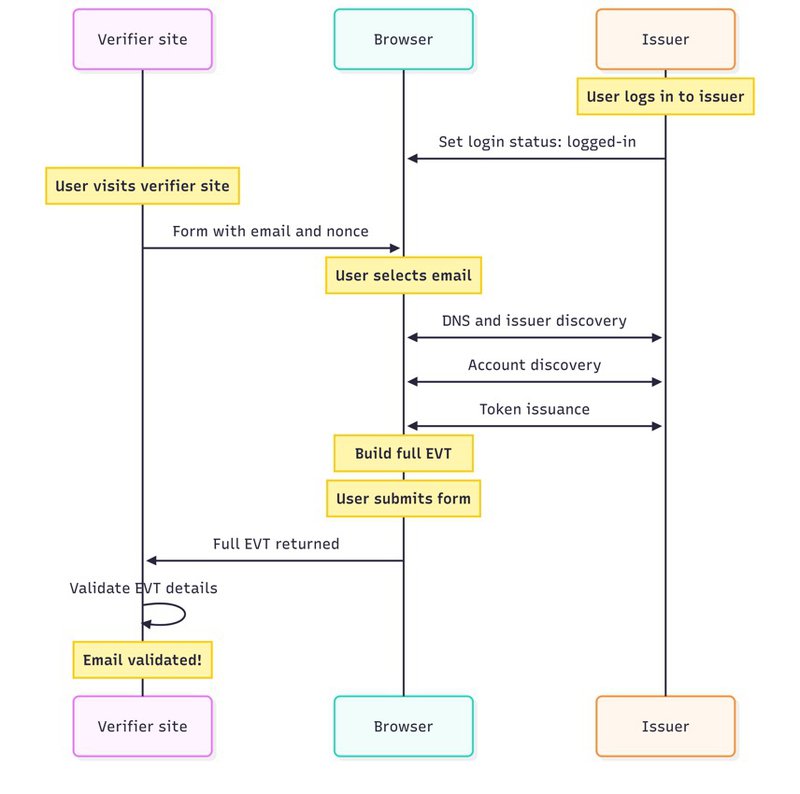
None of these steps require the site to send a single email. Gmail is participating in the origin trial as a launch provider, meaning any @gmail.com address can be tested through the flow without additional provider-side configuration, which gives the trial an immediate, meaningful test population.
Why This Matters for Deliverability and Marketing Teams
The Email Verification Protocol is still an experimental, Chrome-specific origin trial, not a finished standard, and it's worth treating it that way. But a few practical implications are worth tracking now rather than after it ships broadly:
- Fewer transactional verification sends. If EVP adoption grows, sites could send meaningfully fewer OTP and magic-link emails for sign-up and account recovery flows, which changes transactional sending volume without changing marketing campaign volume.
- Reduced friction at signup. Removing the "check your inbox" step is a conversion improvement for verifier sites, independent of anything related to deliverability itself.
- No change to sender authentication requirements. The Email Verification Protocol does nothing to satisfy SPF, DKIM, or DMARC requirements, and Gmail and Yahoo's bulk sender authentication rules remain entirely unaffected by it.
- EVP depends on browser support, participation from the email provider, and a correctly implemented verification flow. Manually entered email addresses can also trigger the process in supported Chrome versions. The verifier site must therefore be prepared to fall back to standard email confirmation whenever the required conditions are not met or the verification token is missing or fails validation.
While EVP may change how websites verify email ownership, it does not show whether your outbound emails are reaching inboxes or being filtered as spam. Before sending your next campaign, run a free Email Deliverability Test with Mailora to review inbox placement, authentication, and other important deliverability signals.
Common Misconceptions to Avoid
The Email Verification Protocol is not a replacement for DMARC, SPF, or DKIM, and adopting it does not directly improve inbox placement or sender reputation. It is still an experimental feature being tested through Chrome's origin trial, with support available on desktop and Android in the documented Chrome versions. Gmail is a documented participating provider, but this does not mean that all email providers support the protocol. Most users may still need traditional verification methods if their browser, email provider, or website implementation does not meet the required conditions. Finally, EVP confirms that a user has an active session with their email provider; it does not guarantee that future marketing or transactional emails will reach the inbox. Inbox placement still depends on factors such as authentication, sender reputation, engagement, and message content.
Latest Developments in Google's Email Verification API
Google's Email Verification API continues to evolve through Chrome's origin trial, with updates focused on browser compatibility, verification workflows, and implementation requirements. The proposal aims to make email ownership verification easier by allowing supported browsers to communicate with participating email providers instead of requiring users to open a separate verification email.
Here are the latest developments that website owners, developers, and email marketing teams should understand.
Chrome Desktop and Android Support
The Email Verification origin trial initially started in Chrome 150 for desktop. Support was subsequently extended to Android beginning with Chrome 154.
According to Google's current documentation, the origin trial runs through Chrome 160 on desktop and Chrome 160 on Android, starting from Chrome 154.
This expands the potential reach of the feature, although it does not mean that every Chrome user can use it. The browser, email provider, user session, and website implementation must meet the required conditions.
Support for Manually Entered Email Addresses
An important improvement is that users do not have to select their email address exclusively from browser autofill suggestions.
Chrome 151 introduced support for email addresses entered manually. Users can type or paste an address and leave the email field to trigger the verification process.
This makes the experience more flexible for users who prefer entering their email addresses themselves.
Participating Email Providers
The protocol depends on participation from email providers that can verify the user's active account session and issue a signed Email Verification Token (EVT).
Gmail is a documented participating provider in the origin trial. Users can test the experience with a Gmail address when signed in to the corresponding Google Account in the same Chrome browser profile.
However, this should not be interpreted as universal support across email providers. Websites must continue supporting their existing verification methods for addresses and providers that cannot complete the browser-based process.
Changes to the Verification Flow
Google has continued refining the technical implementation based on developer feedback.
Some notable updates include:
- Chrome 153 introduced HTTP Message Signatures for token issuance requests
- Chrome 154 updated the
Sec-Fetch-Destheader value toemail-verification - Chrome 154 introduced support for third-party origin trials, subject to issuer-domain requirements
- Chrome 156 changed the email claim to return the address as entered in the form, rather than necessarily returning a canonicalized version
These changes matter primarily to developers and email providers implementing the protocol. They also demonstrate why websites participating in the origin trial need to follow the latest implementation documentation.
Origin Trial Status and Implementation Considerations
The Email Verification API remains an experimental feature available through Chrome's origin trial. It is not yet a universally available replacement for conventional email verification.
Google's October 2026 update states that it does not anticipate further breaking changes and is preparing to ship the feature. However, its current documentation still cautions that backward-incompatible changes may occur as development continues.
Websites testing the feature should also review their origin trial registration. Tokens generated before the trial extension expire on November 17, 2026, and affected websites must renew and redeploy their tokens.
What Website Owners and Email Marketers Should Know
The development of browser-based email verification could reduce friction during account registration, newsletter subscriptions, checkout, and other email collection processes.
However, it does not remove the need for a broader email strategy.
Email ownership verification and email deliverability serve different purposes. The protocol helps establish that a user controls an email address through a participating provider. It does not establish whether future emails will reach the inbox, whether the address will remain active, or whether a sender has correctly configured SPF, DKIM, and DMARC.
For email marketing teams, the practical approach is to monitor the protocol's development while maintaining existing verification workflows, email authentication practices, and deliverability monitoring.
Conclusion
The Email Verification Protocol introduces a different way to confirm email ownership: through a browser-mediated verification process rather than a traditional email message. It does not replace SPF, DKIM, or DMARC, and it does not guarantee inbox placement or improve sender reputation. Although the technology is progressing through Chrome's origin trial, broader browser and email provider support remains an important consideration.
For businesses that rely on OTP and magic-link emails for registration, onboarding, or account recovery, EVP is worth monitoring as it develops. However, reducing verification emails does not remove the need to maintain strong email authentication and deliverability practices.
Before sending your next campaign, use Mailora's free Email Deliverability Test to review important deliverability signals, including email authentication and inbox placement.
Frequently Asked Questions
Q1. Does the Email Verification Protocol replace SPF, DKIM, or DMARC?
No. The Email Verification Protocol confirms a user controls an email address at the moment they submit a form. SPF, DKIM, and DMARC authenticate outbound mail in transit. They solve different problems and neither replaces the other.
Q2. Which browsers and email providers support the Email Verification Protocol today?
The Email Verification Protocol is currently being tested through Chrome's origin trial. The trial began on desktop with Chrome 150 and expanded to Android starting with Chrome 154. Google's documentation lists support through Chrome 160 on both platforms. Gmail is a documented participating provider, but broader support from other email providers and browsers has not been confirmed. Websites should continue offering traditional email verification as a fallback.
Q3. Will adopting the Email Verification Protocol improve my email deliverability?
Not directly. It can reduce how many verification emails you send and improve signup conversion by removing friction, but it has no effect on sender reputation, authentication, or inbox placement for the campaign and transactional email you continue to send.
Q4. Do I need a fallback if I implement the Email Verification Protocol?
Yes. Because there's no feature detection and EVP only triggers under specific browser and user conditions, every implementation needs a fallback to a standard email confirmation flow whenever the verification token isn't present or fails validation.
Learn how Mailora helps you monitor the deliverability fundamentals, authentication, reputation, and engagement, that remain essential no matter how email verification at signup continues to evolve.
Sources: Rowan Merewood, "Test the Email Verification Protocol with an origin trial," Chrome for Developers Blog, published July 8, 2026.
Stay in the loop
Deliverability insights, product updates, and early access to new features. No spam, unsubscribe anytime.
By subscribing, you agree to our Privacy Policy. Unsubscribe anytime.